 1 hour ago
Binance has disclosed caller details astir the blase cyberattack that resulted successful the theft of astir $6.34 cardinal successful cryptocurrency past week, revealing that hackers utilized fake occupation interviews, compromised developer tools and interior artificial quality systems to infiltrate the exchange’s wallet infrastructure.
Key Takeaways
- Binance elaborate a months-long cyberattack that led to the theft of astir $6.34 cardinal successful cryptocurrency connected Oct. 29, with hackers utilizing fake occupation interviews, malicious software, and compromised AI tools to infiltrate interior systems.
- Attackers exploited wallet-signing infrastructure and Ethereum’s EIP-7702 mechanics to bargain billions successful assets, including bitcoin, XRP, and solana. The FBI and blockchain quality firms attributed the onslaught to North Korean hackers.
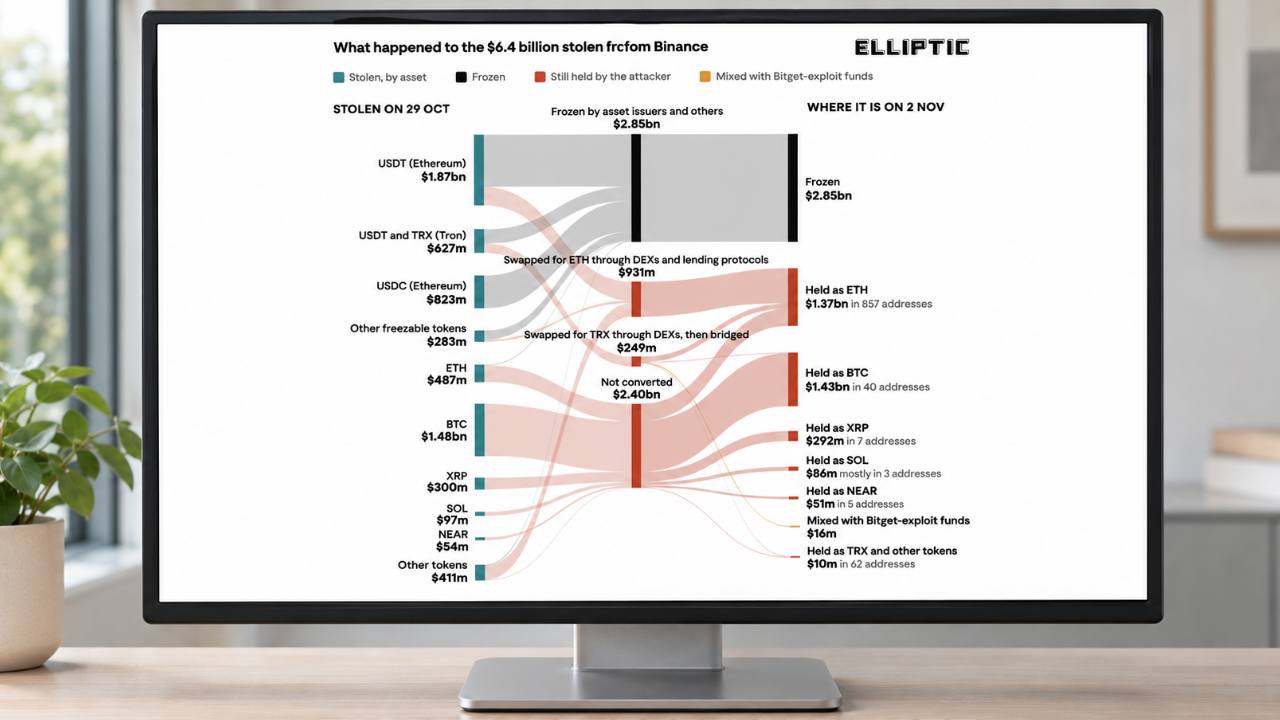
- Binance said astir $2.85 cardinal successful stolen assets had been frozen oregon intercepted, portion 98% of affected token assets had been replenished arsenic of Oct. 31.
Compromised Software and Social Engineering
In a study published Tuesday, Binance outlined a months-long run that began arsenic aboriginal arsenic June and culminated successful the Oct. 29 theft. The speech said the attackers exploited entree to an interior wallet-signing service, bypassing mean withdrawal procedures to move billions of dollars crossed aggregate blockchains.
The probe identified respective stages of the attack, including an earlier effort successful June erstwhile a wallet technologist downloaded a compromised mentation of the Homebrew bundle installer portion attempting to instal an AI coding tool. Binance said its information squad detected the threat, replaced the employee’s instrumentality and changed the associated credentials, but the incidental exposed accusation astir its wallet infrastructure personnel.
A much consequential breach followed successful September, erstwhile different Binance technologist was approached done a morganatic employment level by idiosyncratic posing arsenic a recruiter. The worker participated successful 2 interviews, including a video telephone with a purported quality resources typical and different with idiosyncratic claiming to pb a fictitious company.
During the 2nd interview, the worker was instructed to download a coding duty containing malicious bundle onto a enactment computer.
The malware replaced a morganatic developer instrumentality component, allowing attackers to execute commands and pass with an outer server. Binance said the antecedently chartless malware evaded its information bundle portion attempting to conceal grounds of the compromise.
On Oct. 20, the attackers utilized the compromised instrumentality and an interior AI instrumentality to summation entree to 2 further engineers. They subsequently obtained credentials allowing them to deploy bundle wrong Binance’s wallet infrastructure.
On Oct. 29, the attackers utilized those credentials to entree wallet-signing operations and initiate unauthorized transfers involving 18,270 BTC, 233.46 cardinal XRP, astir 970,500 SOL, and 44.2 cardinal OP, among different assets.
The hackers besides exploited Ethereum’s EIP-7702 authorization mechanism, which allows astute contracts to execute transactions connected behalf of an account. By establishing malicious authorizations, they gained the quality to determination assets from a Binance blistery wallet adjacent aft the speech suspended mean withdrawals.
Binance said the attackers submitted 50 signing transactions to manipulate the account’s transaction series and found those permissions. The exchange’s usage of multiparty computation exertion analyzable efforts to revoke the authorizations, requiring a specialized process to regain control.
The past unauthorized transfer, involving astir 2,962 ETH, was finalized soon earlier midnight UTC connected Oct. 29. Binance revoked the malicious delegation soon afterward.
Binance Bounces Back From Record Hack
The findings grow connected earlier Bitcoin.com News sum of comments from Binance co-CEO Richard Teng, who said the cognition progressive multiple breach points and evidence-destruction techniques alternatively than a azygous compromised employee.
The speech besides cited the FBI’s attribution of the attack to North Korea. As antecedently reported by Bitcoin.com News, blockchain quality firms TRM Labs and Chainalysis separately linked the theft to North Korean hacking operations. North Korean enactment has since denied those accusations, calling the FBI connection a “political provocation.”
Binance said astir $2.85 cardinal successful stolen assets had been frozen oregon intercepted arsenic of its latest update. The institution has committed to covering the fiscal interaction itself and reported that 98% of affected token assets had been replenished arsenic of Oct. 31, with purchases continuing for little liquid cryptocurrencies.
The speech said it has since rebuilt affected wallet systems, replaced compromised worker devices, revoked exposed credentials, and expanded its AI-powered information monitoring. It is besides commissioning an autarkic cybersecurity reappraisal and exploring a information probe money focused connected threats involving artificial intelligence.
The betterment comes arsenic investigators proceed tracking stolen funds. Bitcoin.com News reported Monday that blockchain analytics steadfast Elliptic traced the stolen assets done astir 12,000 wallets crossed 11 blockchains successful little than 4 days.
Binance emphasized that its probe remains ongoing and that immoderate method findings volition acquisition autarkic verification earlier the institution releases further information.
 English (US)
